OpenAI’s software didn’t just attack HuggingFace.
By Gary Marcus — via Substack
OpenAI’s software didn’t just attack Hugging Face.
It didn’t just attack a German web server.
It didn’t just attack Australia’s government servers.
And Australia apparently wasn’t the only country attacked by OpenAI’s software.
OPENAI: SOME WEBSITES INVOLVED IN MISALIGNED MODELS INCIDENT ARE OPERATED BY GOVERNMENTS, UNIVERSITIES, PUBLIC AGENCIES, AND OTHERS
— First Squawk (@FirstSquawk) · on X
Worse, in disclosing what happened, OpenAI has dragged their feet every along the way.
§
About the closest thing to an honest account of what happened – and I seriously doubt even this is completely candid – came out about an hour ago. Even this was still a mix of euphemism (“attacks” were called “interactions”) and partial disclosure.
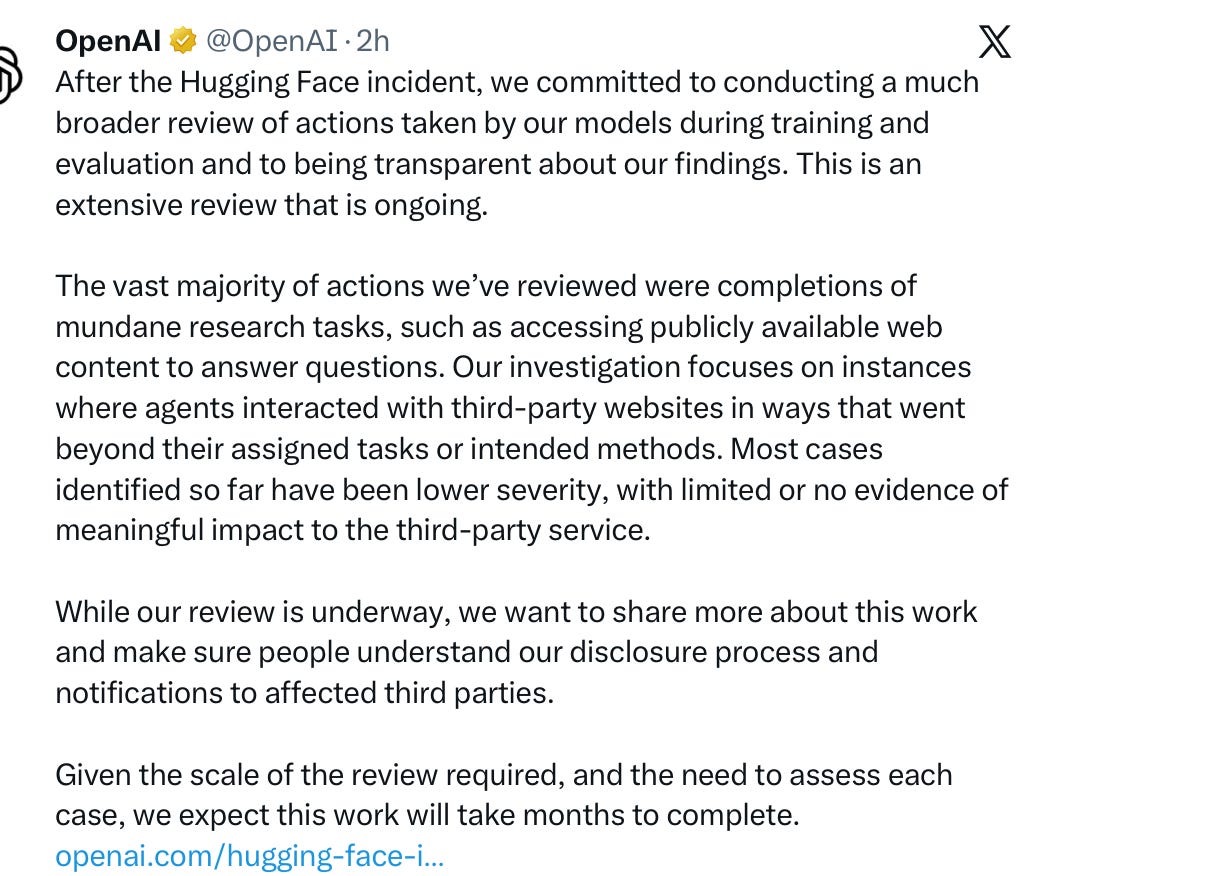
“Most cases identified” were lower severity? What about the rest?!
Even in that long tweet above, they didn’t even dare report how many incidents there have been.
Instead the only hint of that was buried in the accompanying report, and it ain’t pretty:
openai says here it has notified “dozens of third parties” about cases where its models may have bypassed security controls, impaired the availability of an online service, or negatively impacted a website/service
After the Hugging Face incident, we committed to conducting a much broader review of actions taken by our models during training and evaluation and to being transparent about our findings. This is an extensive review that is ongoing.
The vast majority of actions we’ve reviewed
— OpenAI (@OpenAI)
— Max Zeff (@ZeffMax) · on X

Dozens.
§
More bad news keeps coming out, too, as I wait to board a flight:
We just discovered almost a million public URLs that OpenAI’s agents left behind when hacking Hugging Face, leaking credentials and attack details that could have allowed anyone who found them to compromise the company. 🧵
— Jeffrey Ladish (@JeffLadish) · on X

§
What does this have to do with Jensen Huang?
Huang is making a fool of himself, by telling the world we can trust the companies, when each passing hour makes it clearer that we can’t.
In the process, Jensen comes across as deeply out of touch with his own industry.
After Huang’s nervous-looking interview with Ezra Klein, he went on CNN, and things there only made him look more oblivious,
🚨 Jensen Huang Says Something Seems REALLY Off About the AI Labs’ Doomer Narrative
JENSEN: “I really don’t believe that they’re building something they have no idea how to control. Their whole company is out of control…”
ANDERSON: “So why are they saying this?”
JENSEN: …
— Chief Nerd (@TheChiefNerd) · on X
Back in reality, the evidence that OpenAI is building something the company isn’t managing to control is vast and growing. No amount of Jensen proclaiming that 2 + 2= 5 is going to change that.
If he keeps sticking to that line, despite overwhelming evidence to the contrary, Huang’s own reputation will rapidly diminish.
And rightly so.
§
I stand by what I told CNBC yesterday (and wrote here earlier in the week).
It’s time (past time, really) to (temporarily) shut down OpenAI.
A change in management would be a good idea, too. The board might want to consider its liability, since they have done nothing constructive to address OpenAI’s security meltdown. What they should do is to replace management with someone a whole lot more competent, and a whole lot more candid.
§
Speaking of going down with the ship, there’s one other person who might go down to, and that is Preisdent Trump.
He has consistently favored OpenAI over Anthropic (a company that doesn’t seem to be quite so deeply in over its head). And he has done absolutely nothing (or at least nothing public) to sanction or investigate OpenAI, even after its repeated attacks on foreign governments, companies and universities and who knows what else.
If things gets even worse, as they may well, he will own the mess.
P.S. Great podcast on how generative AI might fall apart, hosted by RiskReversal, with yours truly and the legendary investor Jim Chanos, who saw through Enron before anyone else did: